Auto-generate Flow Chart from Java/C++ Codes:

Raptor Flowchart Tutorial For Beginners

Wednesday, October 23, 2013

AmBank security guard shoots colleague dead in robbery

Ditembak mati rakan sekerja sendiri....

(Photo Of The SUSPECT)

BY ELIZABETH ZACHARIAH
OCTOBER 23, 2013
‎A security guard shot dead a bank operations officer in a robbery at the Ambank branch in USJ Sentral, Subang Jaya today.
Noazita Abu Talib, 37, was shot once in the face with a pump-gun in the 6.20pm incident.
It is learnt that the victim was opening the door to the vault‎ when she was shot.
Noazita is a mother of two and had been working at Ambank for 16 years.
The security guard, who fled with an undisclosed amount of cash on a motorcycle, has been identified as a 37-year-old Sabahan with a fake IC.
Subang Jaya deputy superintendant Tan ‎Ah Chua was at the scene when contacted and confirmed the incident. But he declined to elaborate further.
State deputy police chief Datuk Abdul Rahim Jaafar said the suspect was armed and considered to be dangerous, cautioning the public to stay vigil.
Meanwhile, police are looking for Ardi Hamza whose last known address is 70, Jalan Apas, Batu 2, ‎Tawau, Sabah to facilitate investigations. - October 23, 2013.

Tuesday, October 15, 2013

Saturday, October 12, 2013

Google Malaysia Site DNS Hacked

copied from: http://techcrunch.com/2013/10/10/google-malaysia-site-hacked-credit-claimed-by-team-madleets/
-----

Google Malaysia Site DNS Hacked, Credit Claimed By ‘Team Madleets’ Hacker 1337

MATTHEW PANZARINO

Thursday, October 10th, 2013
147 Comments
google
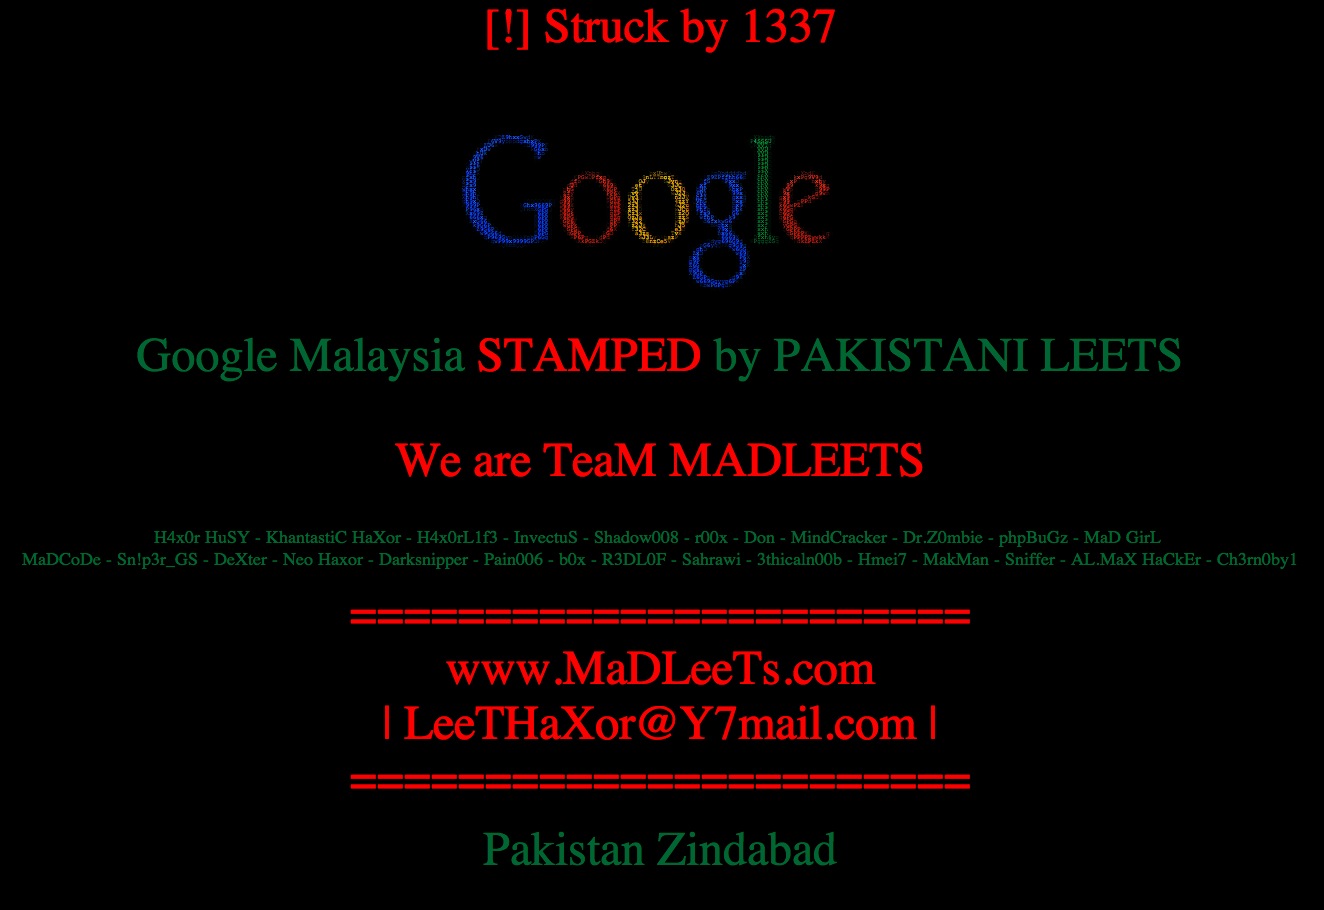
Google’s Malaysian site has been hacked and replaced with a splash screen giving credit to a group called “Team Madleets.” The normal site has been offline for several hours as of late Thursday afternoon and the page lists a series of handles that are ostensibly part of the team responsible.Updated with brief statement from the hackers below.
The attack appears to have been of the DNS poisoning variety, in which a hacker gained access to the Malaysia Network Information Center and changed the DNS records of Google’s site to Madleets-controlled servers. So no information appears to have been changed on Google’s servers at this time, as this is a redirect attack of sorts.
The stamp at the top says ‘[!] Struck by 1337′, which is apparently a reference to an individual hacker within the group called 1337, who has recently (allegedly) performed hacks on domain registrars of several countries. A message on 1337′s Facebook page says “Google Malaysia Stamped By 1337″ and references the google.com.my and google.my domains. The only other indicator about who the group could be is a reference to them being Pakistani in origin.
The Madleets address leads to a Facebook page for the team that has the following message posted:
We feel we need to alert anyone, that we don’t hack any country tlds for example google.com.my as a result of any kind of hate, We don’t hate anyone, We love all humanity, there is no obvious reason for stamping the tlds.
Least the reason is not any kind of hate.
Whatever the reason is we can’t explain except we love all of you.
Regard’s
H4x0rL1f3
The page info states that “MadLeets is a Ethical and 1337 White Hat Hackers Community. We are Anti Hackers , we teach how to protect yourself from getting hacked.”
Screen Shot 2013-10-10 at 3.43.54 PM
If the reasoning on the team’s Facebook page is accurate, then this is simply a matter of doing it because they can and not to make a political statement. A link placed in the source code of the page leads to a music video for the artist Instrumental Core.  The music is auto-played on the site while visitors are there.
Google Malaysia was hacked back in July, along with several other Malaysian sites, by a group protesting the treatment of Bangladeshi workers in that country. One possible motivation for the group taking action now, if it is indeed not simply “exposing vulnerabilities” would be the Global Entrepreneurship Summit in Kuala Lumpur, which will be attended by Secretary of State John Kerry in lieu of President Barack Obama.
We’ve reached out to both the email address given for the team on the site and to Google. We will update this story if we receive a response from either side.
Update: The hackers responded with a brief statement to TechCrunch:
There’s not much reason behind it, only to prove that security is just an illusion. It does not exist.
We have no political intentions whatsoever, as you have already stated.
Regards, LeeT
Catherine Shu contributed additional reporting to this story.

Saturday, September 28, 2013

Microsoft + Nokia = what comes next?


from:http://seattletimes.com/html/localnews/2021743100_microsoftnokiaxml.html
-----

Microsoft buys Nokia’s phone business

Microsoft is paying $5 billion for Nokia’s Devices and Services Business. In addition, it is paying about $2.18 billion to license Nokia’s patents and to license and use Nokia’s mapping services.
Seattle Times staff reporter
MOST POPULAR COMMENTS
HIDE / SHOW COMMENTS
yikes... nokia has been posting losses since they committed to windows os. elop must...  MORE
Balmer just had to waste shareholder money one last time before bowing out. Nokia is a...  MORE
Everyone is falling for the spin here. The previous contract between Microsoft and...  MORE
advertising
Microsoft is buying Nokia’s cellphone handset business as part of a $7.2 billion deal, the two companies announced Monday.
The acquisition represents an aggressive move by Microsoft to compete in the smart-devices market, as the company transforms itself into a devices-and-services business.
“To accelerate our growth in the phone business, we thought it was important to move even faster,” Microsoft CEO Steve Ballmer said in a phone interview.
Microsoft is paying $5 billion for Nokia’s Devices and Services Business. In addition, it is paying about $2.18 billion to license Nokia’s patents and to license and use Nokia’s mapping services.
The businesses that Microsoft is getting from Nokia brought in about $19.7 billion revenue in 2012, about half of Nokia’s sales that year.
Nokia retains other substantial parts of its business, including networking infrastructure and services, technology development and licensing, and mapping and location services.
Microsoft and Nokia, both of which have struggled to compete against Apple and Google Android phones, have been close partners since Nokia announced in February 2011 that it was making Windows Phone its primary smartphone operating system. Its Lumia line of Windows Phone has been credited with Windows Phone’s gain over the past several months, even as the operating system struggles to build beyond its currently worldwide market share of about 3.3 percent
With the acquisition, instead of having to go through two companies for each innovation or marketing move, “we remove any boundaries in agility,” Ballmer said.

Sunday, September 01, 2013

Maksud SuperGlobal - Pembolehubah Global PHP

-----
-
-
Pembolehubah Global PHP  - Superglobals
«Bab sebelumnya        
Superglobals telah diperkenalkan dalam PHP 4.1.0, dan terbina dalam pembolehubah yang sentiasa ada dalam semua skop.
Pembolehubah Global PHP - Superglobals
Beberapa pembolehubah yang telah ditetapkan dalam PHP adalah "superglobals", yang bermaksud bahawa mereka sentiasa diakses tanpa mengira skop - dan anda boleh mengakses mereka dari mana-mana function, class atau file tanpa perlu melakukan apa-apa yang khusus.
Pembolehubah PHP Superglobal adalah:
  • $ GLOBALS
  • $ _SERVER
  • $ _REQUEST
  • $ _POST
  • $ _GET
  • $ _FILES
  • $ _ENV
  • $ _COOKIE
  • $ _SESSION
Bab ini akan menjelaskan beberapa superglobals, dan selebihnya akan diterangkan dalam bab seterusnya.
PHP $ GLOBAL
$GLOBALS adalah sejenis superglobal variable PHP yang digunakan untuk mengakses global variable dari mana-mana tempat dalam skrip PHP (juga dari dalam function atau method).
PHP menyimpan semua pembolehubah global dalam variable yang dipanggil $GLOBALS [index] di mana index itu mewakili nama sesuatu variable.
Contoh di bawah menunjukkan bagaimana untuk menggunakan  $GLOBALS:
Contoh
$x = 75;
$y = 25;

function addition()
{
$GLOBALS['z'] = $GLOBALS['x'] + $GLOBALS['y'];
}

addition();
echo $z;
?>
Dalam contoh di atas, oleh kerana z berada di dalam array $GLOBALS, ia juga boleh diakses di luar function!
PHP $ _SERVER
$_SERVER memegang maklumat mengenai header, path, dan location skrip.
Contoh di bawah menunjukkan bagaimana untuk menggunakan beberapa elemen dalam $_SERVER:
Contoh
echo $_SERVER['PHP_SELF'];
echo "
";
echo $_SERVER['SERVER_NAME'];
echo "
";
echo $_SERVER['HTTP_HOST'];
echo "
";
echo $_SERVER['HTTP_REFERER'];
echo "
";
echo $_SERVER['HTTP_USER_AGENT'];
echo "
";
echo $_SERVER['SCRIPT_NAME'];
?>
Jadual berikut menyenaraikan elemen yang paling penting yang boleh dimasukkan ke dalam $_SERVER:
Element/Code
Description
$_SERVER['PHP_SELF']
Returns the filename of the currently executing script
$_SERVER['GATEWAY_INTERFACE']
Returns the version of the Common Gateway Interface (CGI) the server is using
$_SERVER['SERVER_ADDR']
Returns the IP address of the host server
$_SERVER['SERVER_NAME']
Returns the name of the host server (such as www.w3schools.com)
$_SERVER['SERVER_SOFTWARE']
Returns the server identification string (such as Apache/2.2.24)
$_SERVER['SERVER_PROTOCOL']
Returns the name and revision of the information protocol (such as HTTP/1.1)
$_SERVER['REQUEST_METHOD']
Returns the request method used to access the page (such as POST)
$_SERVER['REQUEST_TIME']
Returns the timestamp of the start of the request (such as 1377687496)
$_SERVER['QUERY_STRING']
Returns the query string if the page is accessed via a query string
$_SERVER['HTTP_ACCEPT']
Returns the Accept header from the current request
$_SERVER['HTTP_ACCEPT_CHARSET']
Returns the Accept_Charset header from the current request (such as utf-8,ISO-8859-1)
$_SERVER['HTTP_HOST']
Returns the Host header from the current request
$_SERVER['HTTP_REFERER']
Returns the complete URL of the current page (not reliable because not all user-agents support it)
$_SERVER['HTTPS']
Is the script queried through a secure HTTP protocol
$_SERVER['REMOTE_ADDR']
Returns the IP address from where the user is viewing the current page
$_SERVER['REMOTE_HOST']
Returns the Host name from where the user is viewing the current page
$_SERVER['REMOTE_PORT']
Returns the port being used on the user's machine to communicate with the web server
$_SERVER['SCRIPT_FILENAME']
Returns the absolute pathname of the currently executing script
$_SERVER['SERVER_ADMIN']
Returns the value given to the SERVER_ADMIN directive in the web server configuration file (if your script runs on a virtual host, it will be the value defined for that virtual host) (such as someone@w3scholls.com)
$_SERVER['SERVER_PORT']
Returns the port on the server machine being used by the web server for communication (such as 80)
$_SERVER['SERVER_SIGNATURE']
Returns the server version and virtual host name which are added to server-generated pages
$_SERVER['PATH_TRANSLATED']
Returns the file system based path to the current script
$_SERVER['SCRIPT_NAME']
Returns the path of the current script
$_SERVER['SCRIPT_URI']
Returns the URI of the current page
PHP $ _REQUEST
PHP $_REQUEST digunakan untuk mengumpul data selepas pengguna menghantar HTML form.
Contoh di bawah menunjukkan satu HTML Form dengan input field dan submit button. Apabila pengguna mengklik pada "Submit", data dihantar kefile yang dinyatakan pada elemen action dalam tag
. Dalam contoh ini, data dihantar kepada 
file yang sama untuk pemprosesan. Jika anda ingin menggunakan file yang lain, gantikan dengan nama file pilihan anda. Kemudian, kita boleh menggunakan superglobal variable $_REQUEST untuk mengumpul data tadi:
Contoh


Name:


$name = $_REQUEST['fname'];
echo $name;
?>
($_REQUEST is a merging of $_GET and $_POST where $_POST overrides $_GET. Good to use $_REQUEST on self refrential forms for validations.)
($_REQUEST adalah gabungan $_GET dan $_POST di mana server akan memberi keutamaan kepada variable $_POST. Sesuai untuk panggilan kepada file sendiri.)
PHP $_POST
PHP $_POST digunakan secara meluas untuk mengumpul data selepas HTML Form dihantar oleh pengguna menggunakan kaedah "post".
Contoh di bawah menunjukkan satu HTML Form dengan input field dan submit button. Apabila pengguna menghantar data dengan mengklik pada "Submit" button, data dihantar kepada file yang dinyatakan pada elemen action dalam
itu. Dalam contoh ini, data di hantar kepada 
file yang sama untuk pemprosesan. Jika anda ingin menggunakan file yang lain, gantikan dengan nama file pilihan anda. Kemudian, kita boleh menggunakan superglobal variable $_POST untuk mengumpul data tadi:
Contoh


Name:


$name = $_POST['fname'];
echo $name;
?>
PHP $_GET
PHP $_GET digunakan untuk mengumpul data selepas HTML Form dihantar dengan menggunakan kaedah “GET”.
$_GET juga boleh mengumpul data yang terdapat di dalam alamat URL.
Andaikan kita mempunyai halaman HTML yang mengandungi link dengan parameter:
Apabila pengguna mengklik pada link "Test $GET", parameter "subject" dan "web" dihantar ke file "test_get.php". Kemudiannya, anda boleh mendapatkan kedua-dua nilai input ini dengan menggunakan variable $_GET.
Contoh di bawah menunjukkan kod dalam "test_get.php":
Contoh


echo "Study " . $_GET['subject'] . " at " . $_GET['web'];
?>

--